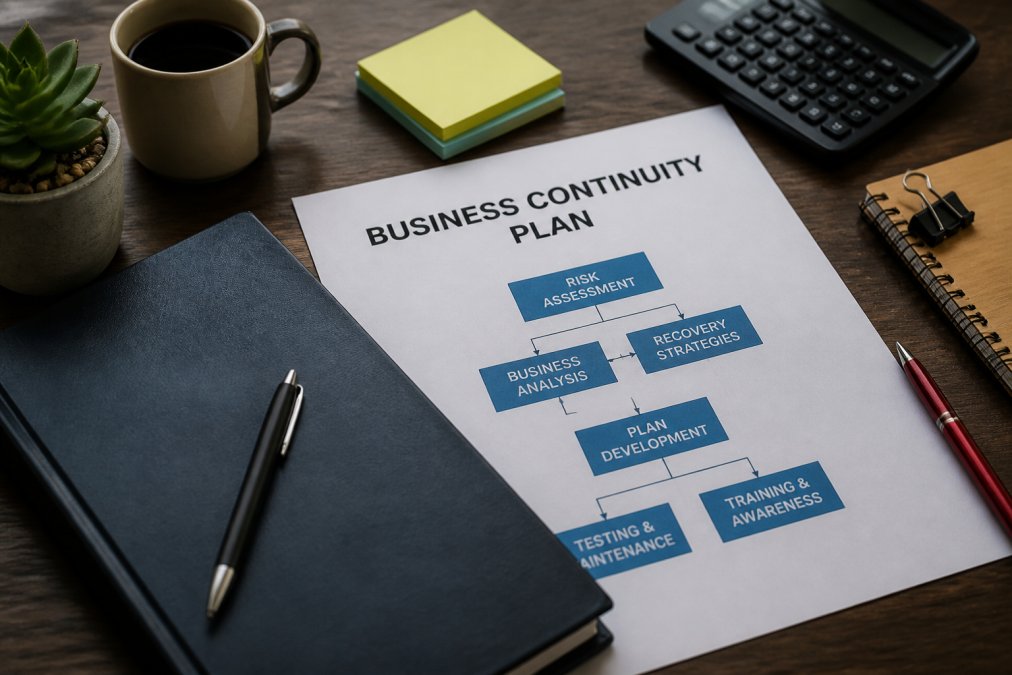
 listicle
7 Best Practices for Business Continuity Planning 2026
Table of Contents
- 7 Best Practices for Business Continuity Planning 2026
- 1. Conduct a Comprehensive Risk Assessment and Business Impact Analysis
- 2. Define Critical Business Functions and Recovery Priorities
- 3. Establish Data Backup and Recovery Strategies with Geographic Redundancy
- 4. Implement Governance Frameworks and Compliance Standards
- 5. Build a Business Continuity Plan Template 2026 Your Team Can Execute
- 6. Master Business Continuity Testing Methods and Simulations
- 7. Develop Communication Protocols and How to Reduce Employee Downtime
- Continuous Improvement and Plan Maintenance
- Frequently Asked Questions
Last Updated: September 24, 2026
7 Best Practices for Business Continuity Planning 2026
Business continuity planning has become essential for companies navigating an unpredictable operational landscape. Organizations that prepare for disruptions, cyberattacks, natural disasters, infrastructure failures, recover faster and maintain stakeholder trust.
A single hour of downtime can cost thousands in lost revenue, damaged customer relationships, and team productivity. Yet many organizations treat business continuity planning as a checkbox exercise rather than a living strategy. This guide covers seven proven practices to prepare, test, and execute a plan that works when crisis hits.
Quick Picks:
- Most Comprehensive Approach: Conduct a full risk assessment and business impact analysis to understand what could fail and what matters most
- Fastest to Implement: Define critical business functions first, this single step clarifies your entire recovery strategy
- Best for Testing Readiness: Use tabletop exercises and simulations to validate your plan before real incidents occur
1. Conduct a Comprehensive Risk Assessment and Business Impact Analysis
A risk assessment identifies what could go wrong. A business impact analysis (BIA) reveals what matters most when it does. Together, they form the foundation of business continuity planning.
List potential threats: cyberattacks, hardware failures, power outages, supply chain disruptions, key personnel loss, natural disasters. For each, estimate likelihood and impact. This forces your team to think through scenarios they'd otherwise ignore.
The BIA maps each business function to its dependencies: systems, data, people, suppliers. Ask: if this function stopped, how long could we operate? How much revenue would we lose per hour? These answers determine recovery priorities.
Rushing through this step results in a plan that protects the wrong things, wasting resources on non-critical systems while neglecting revenue-driving functions.
2. Define Critical Business Functions and Recovery Priorities
Not every business function deserves equal recovery effort. Defining critical functions forces your organization to clarify what it actually depends on.
A critical business function is one that, if lost, would threaten revenue, customer trust, regulatory compliance, or operational viability. Examples: production environment and customer support for software; client communication and billing for professional services; point-of-sale and inventory for retail.
Create a tiered ranking: Tier 1 (recover within hours), Tier 2 (within a day), Tier 3 (within a week). This prevents treating everything as urgent, which drains resources and delays critical recovery.
Assign an owner to each critical function who understands dependencies, knows recovery steps, and can make decisions under pressure. Without clear ownership, you'll waste time figuring out who's responsible.
Review this list annually as your business evolves and critical functions change.
3. Establish Data Backup and Recovery Strategies with Geographic Redundancy
Data loss turns temporary outages into permanent disasters. Your backup strategy must protect against accidental deletion and deliberate attacks.
Implement the 3-2-1 rule: three copies of your data, on two different media types, with one copy stored offsite. This prevents a single failure from destroying everything. Keeping backups on the same server as production data leaves you vulnerable to ransomware or hardware failure.
Geographic redundancy means backups exist in a different physical location from primary systems. Cloud-based solutions handle this automatically, but verify your provider stores copies in geographically separate regions.
Test backups regularly. Schedule monthly restore tests for critical data and document time and issues. Real-world testing reveals problems that theoretical planning misses.
Immutable backups, copies that can't be modified or deleted even by administrators, protect against ransomware. If your business faces cyber threats, immutable backups are essential.
4. Implement Governance Frameworks and Compliance Standards
Governance assigns clear roles, responsibilities, and decision-making authority, the structure that keeps your team organized during chaos.
Define your incident commander, typically a senior operations or IT leader with authority to make fast decisions and mobilize resources. This person coordinates with department heads, communicates with customers, and tracks recovery progress.
Establish escalation procedures: when to activate your full continuity plan, who gets notified, and in what order. Clear escalation prevents overreacting to minor issues or underreacting to serious ones.
Document governance structure in writing with decision trees: "If X happens, do Y. If that fails, escalate to Z." People follow written procedures during crisis, not meeting notes from months ago.
Address compliance requirements relevant to your industry (HIPAA for healthcare, SEC for financial services, ISO for manufacturing). Your continuity plan should explicitly address maintaining compliance during recovery.
Frameworks like ISO 22301 or DRI International's Professional Practices offer proven approaches tested across industries.
5. Build a Business Continuity Plan Template 2026 Your Team Can Execute
A business continuity plan template gives your team a starting point and ensures consistency. Best templates are specific to your operations, not generic.
Include: incident declaration procedures, contact lists, system recovery steps, data recovery procedures, communication templates, and recovery roles. For each critical function, document exact restoration steps.
Make templates actionable. Instead of "restore the database," write: "Log into backup server at [IP]. Run restore script at [path]. Verify integrity by checking [records]. Expected time: 30 minutes."
Include alternative procedures for when primary systems are destroyed or backup servers fail. Secondary recovery paths prevent team paralysis when Plan A fails.
Store templates in multiple locations: printed copies in secure locations and digital copies in cloud storage independent of your internal systems.
Update templates after every incident, even minor ones. Capture lessons while fresh.
6. Master Business Continuity Testing Methods and Simulations
Testing separates plans that work from those that only look good on paper. Different approaches reveal different problems.
Tabletop exercises bring your team together to walk through scenarios. A facilitator presents a crisis and team members discuss response, identify gaps, and document lessons. Fast and low-cost but don't reveal operational problems.
Functional exercises test specific functions by executing failovers to backup systems with test data. This reveals whether procedures work and actual recovery time.
Full-scale simulations test your entire plan under realistic conditions. Expensive and disruptive but catch problems smaller tests miss.
Start with tabletop exercises (low-risk, build confidence), progress to functional exercises for critical systems, reserve full-scale simulations for annual validation.
Document everything during testing: actual recovery time, failed procedures, unclear documentation. These findings show exactly where your plan needs improvement.
7. Develop Communication Protocols and How to Reduce Employee Downtime
When systems fail, communication becomes critical. Employees need to know what's happening, what to do, and when services will be restored.
Establish a communication chain with pre-written templates for different scenarios: "Systems are down, investigating," "Systems are down, recovery timeline is X," "Systems are restored." Templates ensure consistent messaging and save time.
Identify communication channels that work during outages: SMS, phone trees, or external status pages (not email if email is down). Test before you need them.
Train your team on their roles. Tell them: "If systems go down, go to your manager who will direct you to work offline or go home." Clear direction reduces confusion and keeps people productive.
Reducing employee downtime is fundamentally about preparation. When employees know the plan and trust leadership, they stay engaged.
Consider remote work enablement.
Continuous Improvement and Plan Maintenance
Your continuity plan isn't finished when you write it. It's a living document that needs regular updates and refinement.
| Practice | Frequency | Owner | Status |
|---|---|---|---|
| Risk assessment update | Annual | Risk Manager | , |
| Critical functions review | Annual | Operations Manager | , |
| Backup restore test | Monthly | IT Manager | , |
| Tabletop exercise | Semi-annual | Incident Commander | , |
| Compliance audit | Annual | Compliance Officer | , |
| Template update | As-needed | Plan Owner | , |
Frequently Asked Questions
What are the key components of a business continuity plan in 2026?
A modern business continuity plan must include risk assessment and business impact analysis, identification of critical business functions, documented recovery procedures with specific recovery time objectives (RTO) and recovery point objectives (RPO), backup and disaster recovery infrastructure, governance and compliance frameworks, communication protocols, and a testing schedule. The plan should also address remote work enablement. Your plan should be stored in multiple locations and reviewed regularly to reflect changes in your operations.
How often should you update your business continuity planning?
Your business continuity plan should be reviewed and updated at least annually, or immediately after any significant organizational change such as new systems implementation, staff restructuring, or facility relocation. After any incident or simulation exercise, conduct a post-incident review and update the plan with lessons learned. Regular maintenance ensures your plan remains relevant and executable when you need it most.
What's the difference between disaster recovery and business continuity planning?
Disaster recovery focuses specifically on restoring IT systems and infrastructure after an outage, it's the technical component. Business continuity planning is broader and encompasses how your entire organization maintains critical business functions during any disruption, including communication, staffing, supply chain, and operational processes. Business continuity includes disaster recovery as one element, but also covers non-technical aspects like employee safety, customer communication, and alternative work locations.
How do you test a business continuity plan effectively?
Effective testing uses multiple methods: tabletop exercises where teams discuss scenarios without activating systems; simulations that test specific processes in a controlled environment; and full-scale drills that activate actual recovery procedures. Document results, identify gaps, and update your plan based on findings. Testing reveals whether recovery time objectives are realistic, whether staff know their roles, and whether your backup systems actually work. Real-world testing is far more valuable than untested plans.